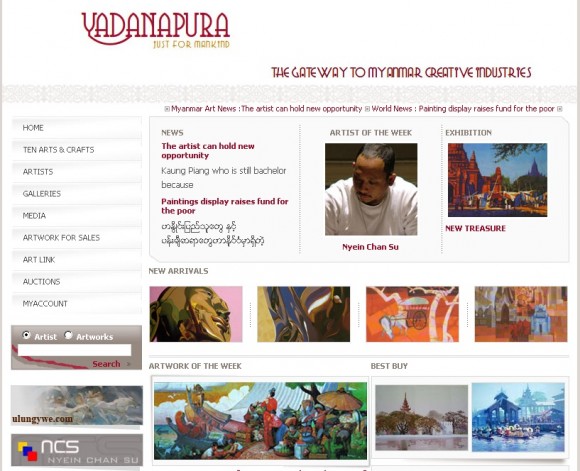
PlanetCreator has reported another critical SQL Injection (vulnerability) on Yadanapura : The Gateway to Myanmar Creative Industries http://www.yadanapura.com powered by IndexMyanmar
This vulnerability has been alerted to :- [email protected]
SQL injection is a code injection technique that exploits a security vulnerability occurring in the database layer of an application. The vulnerability is present when user input is either incorrectly filtered for string literal escape characters embedded in SQL statements or user input is not strongly typed and thereby unexpectedly executed.
Applications: ———— PlanetCreator’s_Universal_Advanced_Internet_Security_T00L
System Time: ———— (UTC+08:00) Yangoon, Myanmar , 18/09/2010 08:28:53 PM
Host IP: 198.68.161.4
Database: yadanapura
Some Tables are as follow :
ydn_weekartwork
ydn_spotnew
ydn_ownership
ydn_newsletters
ydn_member
ydn_mb_artwork
ydn_galdirectory
ydn_for_sale
ydn_feature
ydn_exreception
ydn_exhibition
ydn_exartwork
ydn_artworkstyle
ydn_artworkstatus
ydn_artworkmedium
ydn_artworkdetails
ydn_artnews
ydn_artlink
ydn_artisttype
ydn_artiststatement
ydn_artistopinion
ydn_artistmaster
ydn_artistlist
ydn_artistinterview
ydn_artistfeature
ydn_artistcomment
ydn_adm_pass
We hope that your security staff will look into this issue and fix it as soon as possible.