
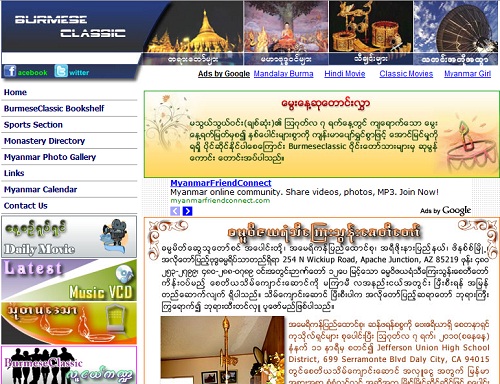
PlanetCreator has reported another critical Blind SQL Injection (vulnerability) on http://www.burmeseclassic.com/
This vulnerability has been alerted to :- Webmaster of BurmeseClassic
Applications: ———— PlanetCreator’s_Universal_Advanced_Internet_Security_T00L
System Time: ———— (UTC+08:00) Yangoon, Myanmar , 07/08/2010 02:28:46 AM
Database :————- burmesec_pawtin
Tables :—————-
youth_qna
youth_news
youth_corner
video_review
video
users
thuta
tayar
sports
song
servers
sayadaw
news
mtv_thingyan
mtv
movies
movie_rate
message
left_menu
health
files
ebook_writer
ebook
dhamma_qus
dhamma_ans
comment
cartoon
buddhawin
baydin_qus
baydin_ans
banned_users
active_users
active_guests
Columns of users table
userip
timestamp
email
userlevel
userid
password
username
username   — password
bcadmin   —– (just for vip members)
We hope that your security staff will look into this issue and fix it as soon as possible.