PlanetCreator reported another critical SQL injection (vulnerability) on several sites of Enjoy (http://www.enjoy.net.mm)
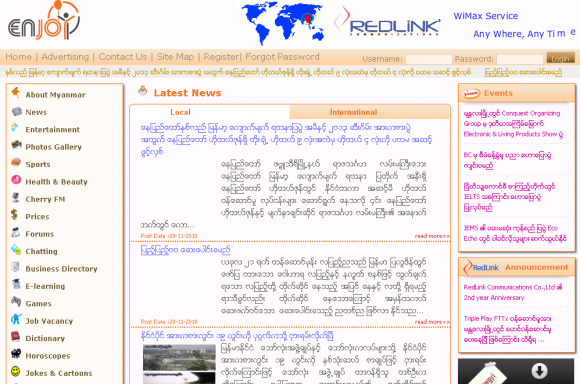
SQL injection is a code injection technique that exploits a security vulnerability occurring in the database layer of an application. The vulnerability is present when user input is either incorrectly filtered for string literal escape characters embedded in SQL statements or user input is not strongly typed and thereby unexpectedly executed.

informed to :-  [email protected]

If you want to see detail of this vulnerability Click Here (Note :- Registered Member Only- If you are not PlanetCreator.Net Member Sign up Here)

We hope that your security staff will look into this issue and fix it as soon as possible.

Explore More

Hackers note to Windows Defender’s Team in Zlob Trojan source code

Russian hacker has sent a note to the windows defender team. It’s discovered by a French analyst while analyzing the variant of the Zlob Trojan. The original note below. “For

Critical SQL Injection in Gulf Travels and Tours

PlanetCreator has reported another critical SQL Injection (vulnerability) on Gulf Tranvels and Tours : Your reliable agency in Myanmar http://www.myanmartravelsgulf.com powered by IndexMyanmar This vulnerability has been alerted to :-

Bruter version 1.0

Bruter is a parallel network login brute-forcer on Win32. This tool is intended to demonstrate the importance of choosing strong passwords. The goal of Bruter is to support a variety